Tag: industrial cybersecurity

  • IEC 62443 Industrial Cybersecurity: A Standards-Based Overview for Manufacturing and OT

    IEC 62443 Industrial Cybersecurity: A Standards-Based Overview for Manufacturing and OT

    Executive summary: What IEC 62443 means for industrial and aerospace operations

    IEC 62443 is the primary international standard family for industrial automation and control systems cybersecurity, published jointly by the International Society of Automation (ISA) and the International Electrotechnical Commission (IEC). The series provides a structured, consensus-based framework for addressing cybersecurity risks across operational technology environments, including process plants, discrete manufacturing lines, and aerospace production and MRO facilities. Its focus on OT security distinguishes it from IT-centric standards like ISO/IEC 27001, reflecting the unique constraints of systems that must maintain real-time performance, safety, and continuous operation.

    The standard family is technology-neutral and sector-independent, meaning it applies equally to oil refineries, water treatment plants, power generation facilities, and aerospace manufacturing cells. Typical OT environments covered include SCADA systems, PLC-based control networks, and distributed control systems that govern everything from chemical process loops to CNC machine tools. This article provides a standards-based overview of IEC 62443: it explains the structure, concepts, and scope of the series, but does not offer prescriptive cybersecurity advice or design recommendations.

    From Connect981’s perspective, IEC 62443 aligns naturally with the operational concerns of aerospace manufacturing and MRO. Digital traceability, controlled workflows, and compliant operations depend on systems where integrity and availability are paramount. Understanding how the standard family defines requirements for industrial networks, control system solutions, and component security provides a useful reference point for organizations managing connected production environments across multiple sites and suppliers.

    Background and purpose of IEC 62443

    Origins in ISA99 and industrial control systems security

    The foundation of IEC 62443 traces back to 2002, when ISA formed the ISA99 committee to address emerging cybersecurity concerns for control systems in critical infrastructure sectors. At the time, industrial control systems were increasingly connected to enterprise networks, yet lacked the security frameworks that had developed for traditional IT systems. The committee brought together engineers, operators, and security professionals to develop consensus-based standards suited to operational technology environments.

    Adoption by the International Electrotechnical Commission

    In the late 2000s and early 2010s, the work of ISA99 was adopted by the IEC, creating the ISA IEC 62443 series recognized internationally. This adoption established a formal pathway for industrial organizations worldwide to reference a common set of requirements and terminology. The collaboration between ISA and IEC continues, with the ISA Global Cybersecurity Alliance and IEC Technical Committee 65 coordinating ongoing development and maintenance of the standard family.

    Purpose and lifecycle coverage

    The purpose of IEC 62443 is to define a common framework for securing industrial automation systems throughout their full lifecycle. This includes design, development, integration, operation, maintenance, and decommissioning. The series creates a shared language for asset owners, automation product suppliers, IACS service providers, and integrators when discussing security requirements, capabilities, and responsibilities. Rather than mandating uniform measures across all assets, IEC 62443 enables organizations to conduct security risk assessment and tailor requirements based on their specific operational risk management profiles and threat environments.

    Scope: What systems and environments IEC 62443 covers

    Defining Industrial Automation and Control Systems

    IEC 62443 defines Industrial Automation and Control Systems (IACS) as systems comprising combinations of hardware, software, networks, and personnel used to monitor, control, and automate industrial processes. This includes distributed control systems, SCADA systems, programmable logic controllers, safety instrumented systems, and the communication networks and software that support them.

    The scope spans multiple layers of industrial architecture:

    • Field devices such as sensors, actuators, and motor drives
    • Controllers including PLCs, RTUs, and embedded control modules
    • Network infrastructure connecting control system components
    • Supervisory systems for process monitoring and management
    • Engineering and maintenance workstations used for configuration and diagnostics

    Covered OT environments

    Typical OT environments addressed by IEC 62443 include process plants in chemicals and refining, discrete manufacturing lines, building management systems, electric power generation and distribution, water treatment facilities, transportation systems, and aerospace production and MRO operations. The standard focuses on cyber-related aspects of availability, integrity, and where relevant confidentiality of automation and control systems, distinct from but complementary to process safety standards.

    IEC 62443 applies to both new installations and legacy systems. Organizations can apply the framework to individual components, integrated systems, or complete facilities. From a Connect981 viewpoint, concrete examples include workstations running digital work instructions, automated test stands interfacing with control systems, specialized MRO benches, and manufacturing cells controlled via PLCs and industrial networks. Each of these represents a system under consideration where cybersecurity requirements must be defined and maintained.

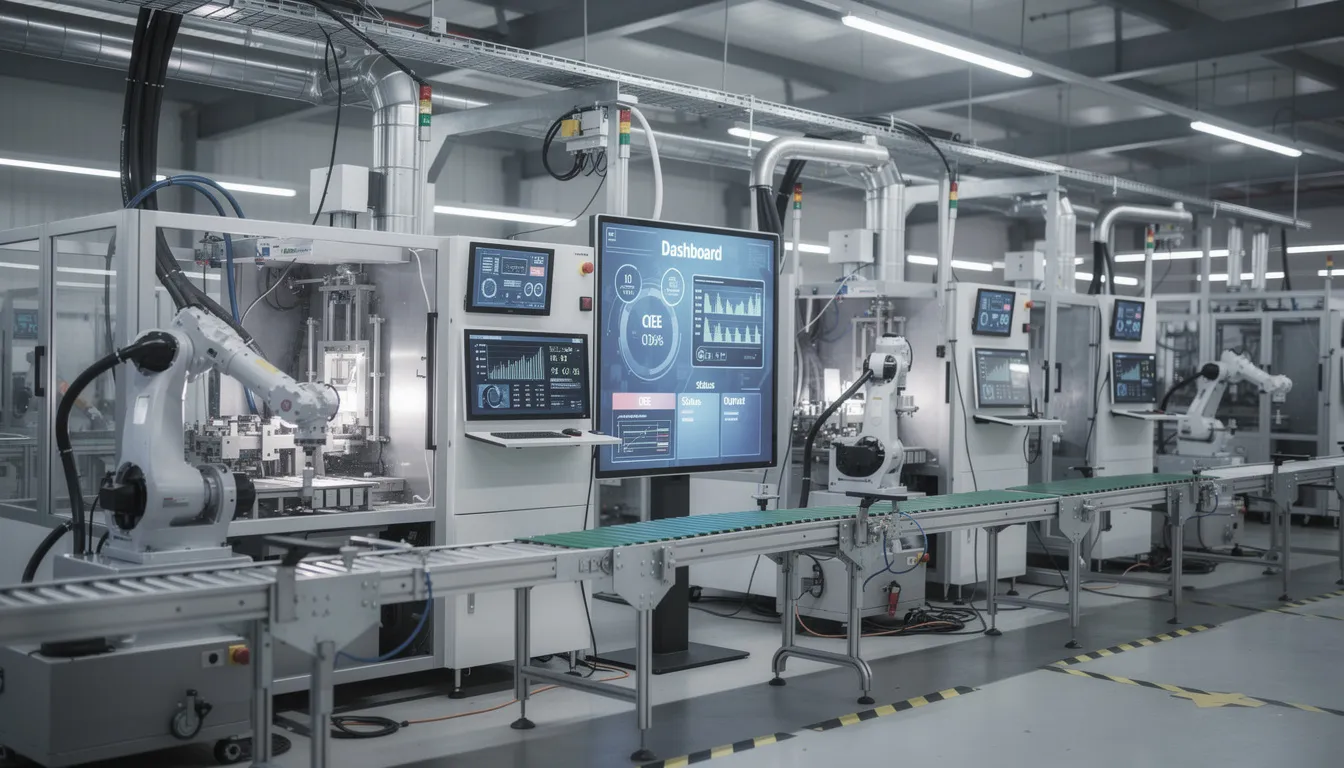
    The image depicts an industrial manufacturing floor featuring robotic arms and control panels actively functioning within a production cell, highlighting the integration of industrial automation and control systems. This environment emphasizes the importance of control systems security and cybersecurity management in operational technology settings to protect critical infrastructure.

    Modular structure of the IEC 62443 standards family

    Four-part architecture

    IEC 62443 is organized into four main groups, each targeting specific roles and abstraction levels within the industrial ecosystem. This modular architecture allows organizations to adopt the most relevant documents first, rather than implementing the entire family simultaneously.

    The General group (part 1-x) establishes foundational terminology, concepts, and models for IACS security. The Policies and Procedures group (part 2-x) defines cybersecurity management system requirements for asset owners and IACS service providers. The System group (part 3-x) addresses system-level security risk assessment and system security requirements for integrated IACS. The Component group (part 4-x) covers secure development lifecycle requirements and technical security requirements for individual components.

    Key documents in the series

    IEC 62443-1-1 introduces the terminology, concepts, and models that form the vocabulary for the entire series. IEC 62443-2-1 specifies security program requirements for establishing and maintaining a cybersecurity management system within an industrial organization. IEC 62443-2-4 defines requirements for IACS service providers system integration and maintenance activities.

    IEC 62443-3-2 provides the methodology for security risk assessment and defining zones and conduits within a system. IEC 62443-3-3 specifies system security requirements and security levels for integrated control systems. IEC 62443-4-1 addresses secure development lifecycle requirements for product suppliers. IEC 62443-4-2 defines technical security requirements for components, establishing component security assurance expectations.

    Relationship between ISA and IEC naming

    The standard family uses parallel naming conventions between ISA and IEC publications. For example, ISA-62443-3-3 and IEC 62443-3-3 contain aligned content. The series collectively spans more than 800 pages of material across technical reports and normative standards. Parts are designed to be used together, but each is formally a separate standard with its own publication and revision cycle, allowing organizations to reference specific editions as required by their governance frameworks.

    Core concepts: Zones, conduits, security levels, and foundational requirements

    IEC 62443 introduces a set of core concepts to describe industrial cybersecurity in a structured, repeatable way. These concepts provide the vocabulary for defining requirements, assessing risks, and aligning expectations among key stakeholder groups without prescribing specific security technologies.

    System under Consideration

    The System under Consideration (SuC) defines the boundary of what is being analyzed or specified. This might be a single production line, a SCADA system for a utility, or a multi-cell aerospace assembly area. Establishing the SuC is a prerequisite for conducting risk analysis and defining security controls appropriate to the operational context.

    Zones and conduits

    Zones are logical groupings of IACS assets that share similar security requirements. A zone might encompass a high-criticality flight-control component machining cell, a lower-criticality facility monitoring network, or an enterprise-facing data collection system. Assets within a zone share a common target security level.

    Conduits are controlled communication paths linking zones. Security requirements for data flows through conduits are defined to manage the transfer of information between areas with different security postures. This approach supports network segmentation strategies that limit the propagation of cyber threats across industrial networks without requiring uniform measures throughout the entire facility.

    Security levels

    IEC 62443 defines security levels (SL 0 through SL 4) as a way to express the required resistance against classes of threat actors. SL 1 addresses protection against unintentional or accidental misuse. SL 2 addresses intentional attacks using simple means and moderate resources. SL 3 addresses sophisticated attacks with significant resources. SL 4 addresses advanced persistent threats with extensive capabilities. Organizations specify target security levels (SL-T) based on risk assessment, and systems or components provide capability security levels (SL-C) that indicate their inherent security features.

    Seven foundational requirements

    Parts 3-3 and 4-2 of the series define seven foundational requirements that structure the detailed system security requirements and technical security requirements:

    • Identification and Authentication Control: Establishing and verifying identity of users, devices, and software.
    • Use Control: Enforcing authorized privileges and least-privilege principles.
    • System Integrity: Protecting systems and data from unauthorized modification.
    • Data Confidentiality: Ensuring sensitive information is protected from unauthorized disclosure.
    • Restricted Data Flow: Controlling and monitoring information flows between zones.
    • Timely Response to Events: Detecting and responding to security incidents.
    • Resource Availability: Ensuring critical systems remain available for intended operations.

    These foundational requirements connect high-level IACS security program requirements with concrete system and component-level expectations.

    Distinguishing IT and OT security in IEC 62443

    Fundamental differences in priorities

    Traditional IT systems environments prioritize data confidentiality, integrity, and availability in roughly that order. Enterprise networks, office applications, and cloud services can typically tolerate brief outages for patching and updates. In contrast, OT systems and operational technology environments prioritize availability and safety above all else. Control systems governing manufacturing processes, utility operations, and safety-critical functions must remain operational continuously. Unplanned downtime in OT environments can disrupt production, damage equipment, or create safety hazards.

    IEC 62443 is explicitly designed around these OT constraints. Long equipment lifecycles, deterministic communication requirements, safety interlocks, and the need for continuous operation shape how security measures are interpreted and applied. The standard recognizes that aggressive patching cycles and frequent system restarts, common in IT environments, may be impractical or dangerous in operational technology environments.

    Shared concepts with OT-specific interpretation

    The standard family still addresses IT security concepts such as authentication, logging, data protection, and access control. However, IEC 62443 interprets these concepts in a way that reflects OT-specific requirements and risk trade-offs. For example, identification and authentication controls must function reliably without introducing latency that could disrupt real-time control loops.

    Aerospace and MRO examples

    In aerospace manufacturing and MRO operations, the IT/OT distinction manifests in concrete scenarios. A CNC machine tool cell where unplanned downtime disrupts flight hardware deliveries represents a high-availability OT environment. A test stand where control software interacts with high-energy systems subject to process safety standards requires careful integration of cybersecurity and safety requirements. Shopfloor terminals running digital work instructions may interface with both MES and ERP systems (IT) and machine controllers (OT), creating convergence points where both perspectives apply.

    IEC 62443 provides a vocabulary to align IT security teams, OT engineers, and production management. The standard defines roles and shared concepts without prescribing a particular organizational structure, enabling organizations to coordinate control systems cybersecurity standards across functions.
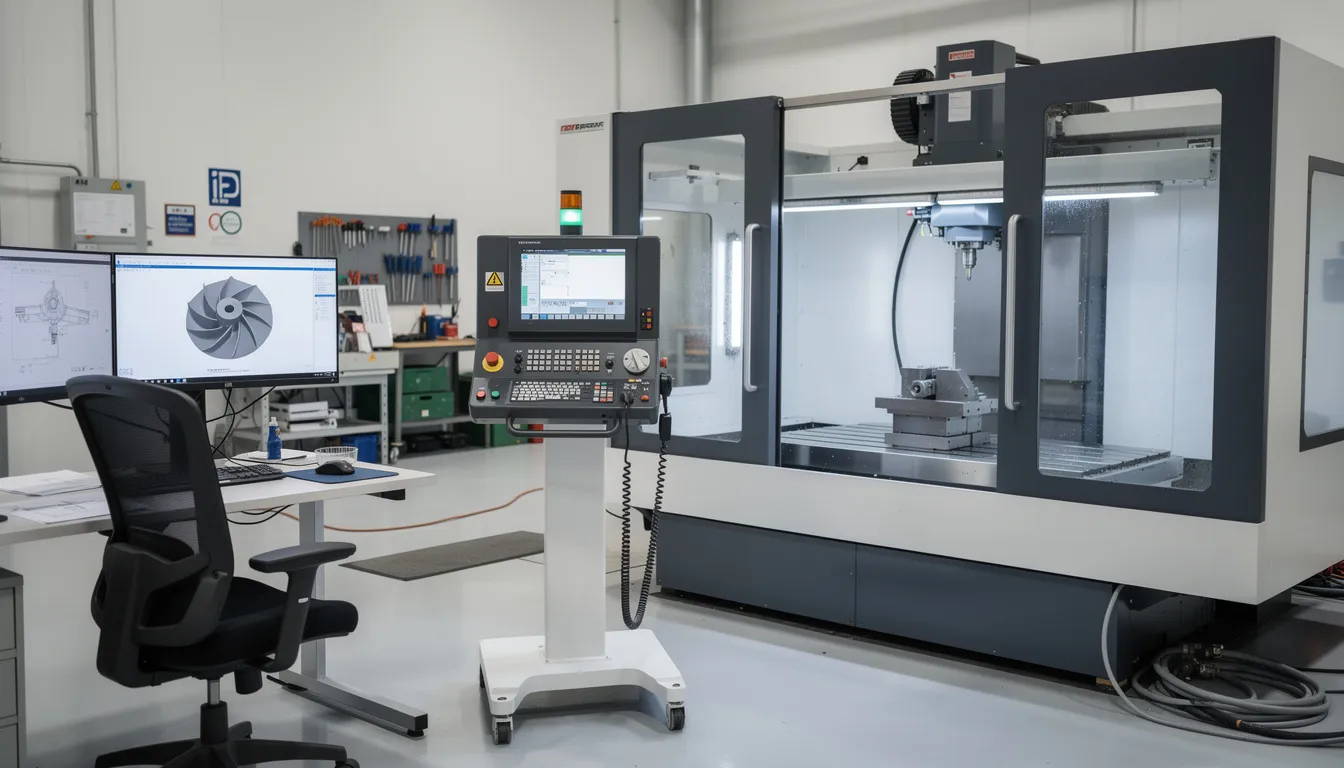
    The image depicts an aerospace CNC machining center featuring an operator workstation and an industrial control panel, illustrating a sophisticated setup for industrial automation. This environment emphasizes the importance of control systems security and operational technology, highlighting the need for robust cybersecurity measures in critical infrastructure.

    Relevance of IEC 62443 for manufacturing, aerospace, and MRO operations

    Connectivity and convergence in modern manufacturing

    IEC 62443 is particularly relevant for modern manufacturing and aerospace operations where OT systems are increasingly connected to enterprise IT, supplier networks, and cloud-based analytics platforms. Industry 4.0 initiatives have expanded the attack surface for industrial automation control systems, making structured approaches to OT security essential. The standard provides a framework for addressing cybersecurity risks that arise when production systems, work instructions, and quality data flow across previously isolated boundaries.

    Supporting key manufacturing concerns

    The framework supports several operational concerns central to aerospace manufacturing and MRO:

    • Maintaining predictable production schedules and turnaround times by protecting control systems that govern manufacturing execution
    • Protecting integrity of process parameters, digital work instructions, and test results that feed quality and compliance records
    • Ensuring traceability and auditability of control changes across facilities and suppliers participating in complex programs

    Connection to aerospace regulatory and quality frameworks

    Aerospace operations already navigate regulatory and quality frameworks including AS9100, FAA and EASA oversight, NADCAP audits, and ITAR requirements. IEC 62443 provides complementary IACS-focused expectations for critical infrastructure protection, but does not replace sector-specific regulations. The standard’s structured approach to defining zones, security levels, and security requirements can support regulatory compliance efforts by establishing consistent terminology and expectations for industrial automation and control systems security.

    Connect981 perspective on IEC 62443 alignment

    From Connect981’s perspective, a unified operations layer that connects ERP, MES, documentation, and shopfloor execution benefits from alignment with IEC 62443 concepts. Clear definition of systems and zones across multiple plants and suppliers supports consistent governance. Structured handling of configuration data and production records feeding traceability and quality systems reflects the integrity requirements central to the standard. Integration of supplier data and remote services into the broader OT and IT systems landscape can reference the conduit and zone concepts to maintain appropriate security controls.

    Concrete manufacturing scenarios illustrate this relevance. A multi-site wing assembly program with shared routing and inspection workflows spans multiple zones, each with defined security requirements. An MRO facility managing serialized components with long service histories and distributed data sources must maintain control system solutions that protect the integrity of maintenance records across the component lifecycle.
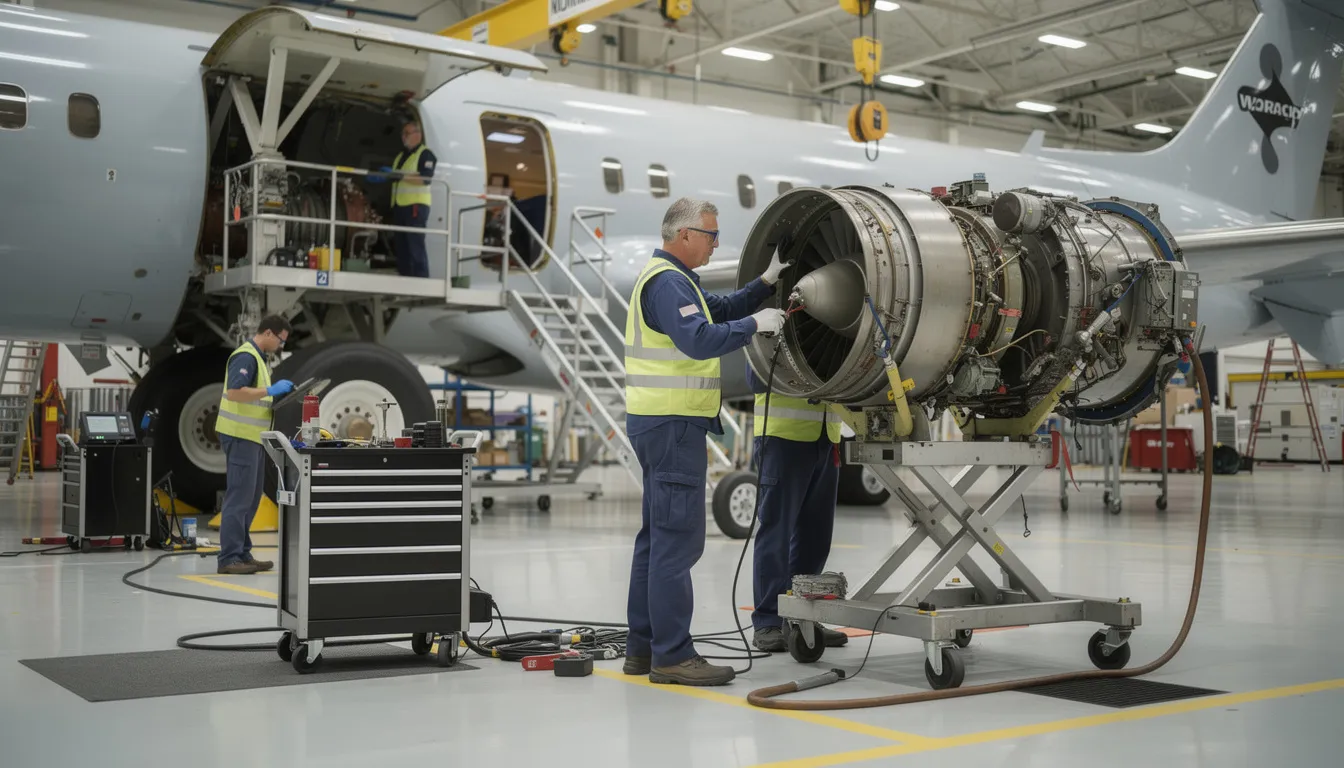
    The image depicts MRO technicians diligently working on various aircraft components within a spacious hangar environment, showcasing their expertise in maintaining control systems and ensuring the safety of critical infrastructure. The scene highlights the importance of industrial automation and control systems in aviation maintenance, emphasizing the need for robust cybersecurity practices to protect operational technology.

    Roles and responsibilities across the industrial ecosystem

    Stakeholder categories in IEC 62443

    IEC 62443 assigns expectations to different stakeholder groups involved with IACS. The standard recognizes that industrial cybersecurity is not the responsibility of any single party, but rather emerges from coordinated efforts across asset owners, product suppliers, system integrators, and service providers.

    Asset owner responsibilities

    Asset owners, typically the organizations operating industrial facilities, define required security levels for their systems based on security risk assessment. They establish and maintain a cybersecurity management system, coordinate cybersecurity practices across sites, and implement continuous monitoring and response capabilities. Asset owners are responsible for ensuring that the combined system meets target security levels, even when integrating components from multiple suppliers.

    Product supplier responsibilities

    Product suppliers, including OEMs of control system components, design and document component security capabilities in line with IEC 62443-4-1 and 4-2. Secure development lifecycle requirements ensure that products are designed with security in mind from the outset. Suppliers document the security levels components can achieve and provide information needed for integration and operation.

    Integrator and service provider responsibilities

    System integrators combine components from multiple suppliers into systems that meet defined security requirements. They are responsible for ensuring that the integrated system achieves the target security levels specified by asset owners. IACS service providers, including those providing maintenance, engineering, and remote support, must meet requirements defined in IEC 62443-2-4 for documentation, testing, and lifecycle support.

    Coordination in aerospace environments

    In aerospace manufacturing and MRO environments, multiple parties must coordinate around consistent terminology and requirements. Internal engineering teams, external equipment OEMs, specialized MRO service providers, and digital platform vendors all contribute to the security posture of connected production systems. IEC 62443 provides the shared vocabulary that enables this coordination without prescribing specific organizational structures.

    Integration with broader standards and governance frameworks

    IEC 62443 is often used alongside other international and sectoral standards. ISO/IEC 27001 addresses information security management for enterprise IT systems. The NIST Cybersecurity Framework provides a risk-based approach applicable across sectors. Process safety standards such as IEC 61511 address functional safety for industrial processes. Each covers distinct but related domains.

    IEC 62443 focuses specifically on IACS and OT, while ISO/IEC 27001 primarily addresses information security for enterprise IT. Organizations commonly map requirements between these frameworks to achieve unified governance across IT and OT environments. The zone and conduit concepts from IEC 62443 can complement higher-level risk and compliance frameworks, providing specific vocabulary for industrial networks and critical systems within broader governance structures.

    For aerospace operations already managing AS9100, FAA, EASA, and ITAR compliance, IEC 62443 offers additional structure for addressing cybersecurity risks in production and MRO environments. The standard’s terminology for security levels, foundational requirements, and system security assurance can support audit readiness and consistent reporting across industry sectors.

    From the perspective of a connected operations platform like Connect981, aligning data models and workflows with IEC 62443 concepts supports consistent reporting, documentation, and audit readiness across factories, MRO facilities, and suppliers. The framework provides a reference for coordinating digital workflows and external networks without creating conflicts with existing regulatory compliance requirements.

    Practical considerations and limitations when applying IEC 62443

    Phased adoption

    The IEC 62443 series is extensive, covering hundreds of pages across multiple parts. Organizations typically phase their adoption according to role and priority. Asset owners may begin with IEC 62443-2-1 to establish a cybersecurity management system, while product suppliers focus on IEC 62443-4-1 and 4-2 for secure development and component requirements. This modular approach allows organizations to adopt the most relevant documents first without requiring simultaneous implementation of the entire family.

    Contextual factors in industrial environments

    Industrial plants and aerospace operations present contextual factors that affect how IEC 62443 requirements are interpreted and applied. Prevalence of legacy control systems with limited security capabilities, heterogeneous vendor landscapes spanning multiple generations of equipment, and multi-decade asset lifecycles all influence implementation approaches. The standard family intentionally leaves room for organizations to interpret and implement requirements in line with their own risk governance and operational constraints.

    Ongoing evolution of the standard

    Different parts of the standard family mature at different times, with revisions and new technical reports periodically published through the IEC and ISA. Organizations must track applicable editions and updates to ensure their practices remain aligned with current expectations. The ISA Global Cybersecurity Alliance continues to coordinate development and provide guidance on applying the series across industry sectors including the industrial process sector, discrete manufacturing, and critical infrastructure.

    Conclusion: IEC 62443 as a reference point for secure industrial operations

    IEC 62443 provides a structured, role-aware framework for describing and specifying cybersecurity requirements for industrial automation and control systems across industries. The series establishes clear scope, modular structure, and core concepts including zones, conduits, security levels, and seven foundational requirements. The explicit distinction between IT and OT security ensures that the framework addresses the unique constraints of critical functions in operational technology environments.

    For manufacturing, aerospace production, and MRO operations, IEC 62443 offers particular relevance. Digital traceability, controlled workflows, and cross-site consistency depend on systems where integrity and availability are paramount. The framework provides vocabulary and expectations that support coordination among engineering, operations, suppliers, and enterprise governance functions managing critical assets across complex programs.

    From Connect981’s perspective, standards such as IEC 62443 form a foundational reference for designing and governing digital industrial operations. The framework enables alignment between operational technology security requirements and the connected workflows that define modern aerospace manufacturing and MRO, supporting organizations as they maintain control system solutions that meet evolving expectations for industrial cybersecurity.
  • NIST 800-53 Security Controls: Catalog Overview and Industrial Context

    NIST 800-53 Security Controls: Catalog Overview and Industrial Context

    What is NIST SP 800-53?

    NIST Special Publication 800-53, Revision 5, finalized in September 2020, is a comprehensive catalog of security and privacy controls for information systems and organizations. Published by the National Institute of Standards and Technology, this document provides over 1,000 individual security controls organized across 20 control families. The catalog serves as a structured reference for describing, documenting, and evaluating safeguards that protect organizational operations, data, and systems from a range of threats including hostile attacks, natural disasters, structural failures, and insider threats.

    The publication was originally developed for U.S. federal information systems subject to the Federal Information Security Management Act. However, Revision 5 deliberately removed the word “federal” from its title and scope language, positioning NIST 800-53 as a broadly applicable control catalog. This shift reflects the reality that federal government agencies, defense contractors, critical infrastructure operators, and private sector organizations increasingly share common security requirements and benefit from a unified vocabulary for describing expected safeguards.

    NIST SP 800-53 is maintained by the Joint Task Force, which includes representatives from civil, defense, and intelligence communities. The catalog itself does not prescribe how an organization must implement controls. Instead, it enumerates standardized control statements, organizes them into families, and provides discussion and enhancement options for each. This article is a descriptive overview of the catalog and its role in federal and industrial contexts, not a guide to selecting or implementing controls or achieving compliance.

    Key attributes of NIST 800-53 as a catalog:

    • Contains over 1,000 security and privacy controls
    • Organized into 20 distinct control families
    • Provides base controls and optional control enhancements
    • Technology-neutral and adaptable to different system types
    • Serves as a reference vocabulary, not a rigid compliance checklist
    • Maintained by NIST with input from multiple federal communities

    The image depicts a secure modern data center featuring rows of server racks illuminated by blue lighting, emphasizing the importance of security controls and risk management strategies in protecting sensitive data. This environment highlights the implementation of NIST 800 53 security and privacy controls, ensuring robust physical and environmental protection for federal information systems.

    Why NIST 800-53 Exists and How the Catalog is Structured

    The Federal Information Security Management Act of 2002, updated as FISMA 2014, established the requirement for a common, repeatable set of security controls across federal agencies. Before NIST 800-53, agencies often developed their own control sets, leading to inconsistent security posture and difficulty comparing the effectiveness of safeguards across government information systems. The catalog emerged to address this fragmentation by providing a single authoritative reference.

    A control catalog is fundamentally different from a compliance standard or management system. It is an organized, technology-neutral listing of security and privacy safeguards, each with a standardized identifier (such as AC-2 for Account Management or AU-6 for Audit Record Review), a control statement describing the expected behavior, discussion text explaining context and intent, and possible enhancements that add rigor or specificity. The catalog functions as a reference library that organizations can draw from based on their risk management strategy, system categorization, and operational context.

    NIST 800-53 supports the NIST Risk Management Framework by providing the control content that RMF steps reference during system authorization and continuous monitoring. The catalog is divided into 20 control families in Revision 5, covering functional areas such as:

    Family ID

    Family Name

    Focus Area

    AC

    Access Control

    Managing system access and user privileges

    AU

    Audit and Accountability

    Logging and monitoring activities

    AT

    Awareness and Training

    Security training and education

    CM

    Configuration Management

    System baseline and change control

    CP

    Contingency Planning

    Business continuity and recovery

    IA

    Identification and Authentication

    User and device identity verification

    IR

    Incident Response

    Handling security incidents

    MA

    Maintenance

    System upkeep and maintenance controls

    MP

    Media Protection

    Protecting storage media

    PS

    Personnel Security

    Workforce-related safeguards

    PE

    Physical and Environmental Protection

    Facility security

    PL

    Planning

    Security planning documentation

    PM

    Program Management

    Organization-wide security programs

    RA

    Risk Assessment

    Identifying and evaluating risks

    CA

    Security Assessment and Authorization

    Evaluating control effectiveness

    SC

    System and Communications Protection

    Network and data protection

    SI

    System and Information Integrity

    Malware protection and integrity verification

    SR

    Supply Chain Risk Management

    Third-party and vendor risks

    PT

    PII Processing and Transparency

    Privacy controls for sensitive data

    Controls within this framework can be used for both security and privacy purposes. Some controls explicitly address privacy risks and the handling of personally identifiable information.

    Revision 5 Control Families and Key Additions

    Revision 5 represents a major modernization of the catalog to address cloud computing, cyber physical systems, mobile platforms, and supply chain contexts. Released in September 2020, this revision expanded the control families from 18 to 20, explicitly adding two new families:

    • PT (Personally Identifiable Information Processing and Transparency): Addresses privacy controls including consent management, data minimization, and transparency requirements for handling sensitive data
    • SR (Supply Chain Risk Management): Addresses risks in third-party vendor relationships, software supply chains, and services acquisition processes

    The 20 families span policy, operations, technical safeguards, and program management. Each control family groups conceptually related controls. For example, the access control family covers user access provisioning, remote access logging, account management, and least privilege principles. The configuration management family addresses baseline configurations, change control, and system component inventories.

    The catalog distinguishes between base controls and control enhancements:

    • Base controls represent the minimum safeguard expected to address a particular security or privacy objective
    • Control enhancements build on base controls, adding strength, rigor, automation requirements, or additional conditions

    Organizations must first satisfy base controls before adding enhancements. This structure allows the catalog to serve organizations with varying risk profiles and security requirements.

    NIST SP 800-53B, released alongside Revision 5, provides example security control baselines. These three security control baselines correspond to Low, Moderate, and High impact levels, plus a separate privacy baseline. The baselines suggest which controls and enhancements are appropriate for systems categorized at each impact level. However, the baselines themselves are separate from the catalog and represent one approach to control selection.

    Federal Relevance: FISMA, RMF, and Government Use

    NIST 800-53 serves U.S. federal civilian agencies, the Department of Defense, and the Intelligence Community as the primary security and privacy controls catalog referenced in FISMA-related programs. Federal agencies are required to implement appropriate security controls based on the categorization of their information systems, making the catalog foundational to federal computer security and risk management activities.

    Federal information systems are categorized under FIPS 199, which establishes Low, Moderate, and High impact levels based on the potential adverse effects of a security breach on organizational operations, assets, or individuals. These categorizations point to the control baselines defined in SP 800-53B, which in turn draw specific controls from the SP 800-53 catalog. This tiered approach allows agencies to implement security proportional to the sensitivity and criticality of their systems and data.

    The NIST Risk Management Framework, documented in SP 800-37, uses 800-53 controls throughout its lifecycle steps:

    1. Categorize the system based on mission impact
    2. Select controls from the 800-53 catalog based on categorization
    3. Implement the selected controls
    4. Assess control effectiveness using SP 800-53A procedures
    5. Authorize the system based on risk determination
    6. Monitor controls on an ongoing basis

    Companion publications support different aspects of this process. SP 800-53A provides security assessment procedures for evaluating whether existing controls are implemented effectively. SP 800-53B provides the baseline selections that link system categorization to specific control requirements. These documents work together to form a comprehensive approach to protecting organizational operations and maintaining organizational systems.

    U.S. federal cloud environments, including FedRAMP-authorized offerings, typically map their technical and procedural safeguards back to NIST 800-53 controls as part of their authorization documentation. Cloud service providers seeking to serve federal government agencies document how their services address each required control, creating a shared vocabulary between service providers and agency customers.

    The image depicts a federal government office building prominently displaying the American flag, symbolizing national security and the operational integrity of federal agencies. This structure represents the importance of implementing appropriate security controls and maintaining a robust security posture to protect sensitive data within federal information systems.

    Industrial and Aerospace Relevance Beyond the Federal Sector

    While NIST 800-53 originated for federal systems, Revision 5’s broader language has led to widespread adoption as a reference catalog in critical infrastructure sectors, including aerospace manufacturing and MRO operations. Organizations that never directly interact with federal information systems increasingly encounter 800-53 terminology through their customers, partners, and supply chain relationships.

    Large industrial organizations, primes, and tiered suppliers in aerospace often encounter NIST 800-53 through:

    • Defense contracting requirements: Systems supporting DoD programs may reference 800-53 controls or related publications such as NIST 800-171 for protecting Controlled Unclassified Information
    • Government-funded R&D environments: Research and development operations handling federal data may need to demonstrate alignment with federal security requirements
    • Customer expectations: Primes and major aerospace customers increasingly structure their internal control sets with NIST publications, expecting suppliers to speak the same language
    • Critical infrastructure plan alignment: Aerospace operations often fall under critical infrastructure designations that reference NIST frameworks

    Control areas particularly relevant to aerospace digital operations include:

    Control Family

    Industrial Relevance

    Access Control (AC)

    Shopfloor access, user provisioning, role-based permissions for production systems

    Configuration Management (CM)

    Work instruction version control, system baseline management

    System and Communications Protection (SC)

    Secure data transfer between sites and suppliers, encryption requirements

    Supply Chain Risk Management (SR)

    Supplier data sharing, third-party software components, vendor assessments

    Incident Response (IR)

    Handling cybersecurity risks and security incidents affecting production

    Audit and Accountability (AU)

    Traceability, remote access logging, audit trails for compliance

    From the perspective of a digital operations platform like Connect981, these control areas align with everyday operational concerns. An aerospace operations platform may need to interface with customers that structure their security requirements using NIST 800-53 terminology. Understanding this vocabulary helps bridge conversations between plant managers, IT security teams, and compliance stakeholders when evaluating digital workflows, traceability systems, and supplier data exchange.

    In industrial environments, NIST 800-53 typically serves as a technical reference vocabulary for describing expected safeguards, rather than as a regulatory certification framework. Organizations use it to articulate security objectives and compare approaches across suppliers and partners.

    The image depicts a bustling aerospace manufacturing floor, where workers are actively assembling various aircraft components, surrounded by advanced machinery and tools. This environment emphasizes the importance of security controls and risk management strategies, essential for protecting sensitive data and ensuring the integrity of federal information systems.

    NIST 800-53 and the Nature of Control Catalogs

    A control catalog is a structured, technology-agnostic enumeration of security and privacy controls used to design policies, architectures, and assurance activities. Catalogs like NIST 800-53 provide common language and structure through standardized identifiers, control titles, control statements, and enhancements. They function as neutral building blocks without dictating specific tools, products, or implementation tactics.

    NIST 800-53 distinguishes between controls operating at different organizational levels:

    • Organizational or program-level controls (PM, PL): Address organization’s security planning policies, information security program plan development, and program management activities
    • System-level technical safeguards (SC, SI): Address communications protection, information integrity, malware protection, and system security functions
    • Human-centric or process-oriented controls (AT, PS, IR): Address security training, personnel security, and incident response procedures

    The catalog covers both security functionality and assurance. From a functionality perspective, controls describe what safeguards should do, such as enforce access restrictions or encrypt sensitive data in transit. From an assurance perspective, controls address how organizations verify that safeguards work as intended through security assessment, continuous monitoring, and oversight activities.

    This dual coverage explains why NIST 800-53 is often used when designing assurance programs for complex digital operations. It provides vocabulary for describing both what protections exist and how their effectiveness is evaluated.

    A catalog is fundamentally different from a compliance standard or management system specification:

    Catalog (NIST 800-53)

    Management System Standard

    Enumerates controls and safeguards

    Specifies governance and operational requirements

    Technology-neutral reference

    Defines how to plan, operate, and improve

    Flexible selection based on risk

    Certification against defined requirements

    Building blocks for multiple approaches

    Structured framework for organizational processes

    NIST 800-53 can underpin multiple approaches to security management, serving as a reference that different frameworks and programs draw from according to their specific needs.

    Conceptual Comparison: NIST 800-53 and ISO/IEC 27001

    ISO/IEC 27001, most recently updated in 2022, is an international standard that defines requirements for an Information Security Management System. The standard is supported by a control set in Annex A, which is linked in detail to ISO/IEC 27002. While both NIST 800-53 and ISO 27001 address information security, they operate at different layers and serve different purposes.

    NIST 800-53 is a detailed control catalog containing hundreds of individual security and privacy controls organized into 20 families. It provides granular control statements that describe specific safeguards, behaviors, and technical requirements. The catalog is designed to be selected from and tailored based on system categorization and organizational risk assessment.

    ISO/IEC 27001 is a management system framework specifying how an organization plans, operates, and improves its information security program. It addresses governance, risk management, leadership commitment, resource allocation, and continual improvement. Annex A provides a structured but shorter list of controls that organizations consider when implementing their ISMS, but the emphasis is on the management system rather than exhaustive control enumeration.

    Key conceptual differences:

    Aspect

    NIST 800-53

    ISO/IEC 27001

    Origin

    U.S. National Institute of Standards

    International Organization for Standardization

    Primary purpose

    Detailed control catalog

    Management system specification

    Control count

    Over 1,000 controls with enhancements

    93 controls in Annex A (2022 version)

    Certification

    No direct certification

    Formal third-party certification available

    Update cycle

    Periodic revisions by NIST

    Periodic revisions by ISO

    Many organizations build internal mappings between NIST 800-53 controls and ISO/IEC 27001 Annex A controls to harmonize terminology. This is common when serving both U.S. federal customers and international commercial clients. The mappings allow organizations to demonstrate that they address security concerns recognized in both frameworks without maintaining entirely separate control documentation.

    Neither framework is inherently better. They serve different purposes. Some organizations use NIST 800-53 as the underlying technical catalog for granular control statements while using ISO 27001 to structure governance, risk management, and continual improvement processes. Others focus primarily on one framework based on their customer base and regulatory environment.

    NIST 800-53, NIST Cybersecurity Framework, and Other References

    The NIST Cybersecurity Framework, first released in 2014 and updated since, organizes cybersecurity activities into five high-level functions: Identify, Protect, Detect, Respond, and Recover. CSF provides a strategic view of security objectives without prescribing specific controls, making it accessible to executives and board members while still useful for technical practitioners.

    CSF profiles often reference NIST 800-53 controls as one of several underlying catalogs that can be used to realize CSF outcomes. Critical infrastructure operators and industrial organizations frequently adopt CSF as their strategic framework while using 800-53 for detailed control statements. This layered approach allows organizations to communicate security posture at multiple levels of abstraction.

    NIST provides mappings between CSF subcategories and 800-53 controls, enabling organizations to:

    • Express high-level security objectives in CSF language for executive communication
    • Retain 800-53 for detailed control statements in technical documentation
    • Trace strategic objectives to specific implemented safeguards
    • Maintain consistency between governance reporting and operational controls

    Similar mapping work exists between 800-53 and other publications:

    • NIST 800-171: Protects Controlled Unclassified Information in non-federal systems, derived from 800-53 with tailoring for contractor environments
    • FedRAMP: Uses 800-53 baselines for cloud service provider authorization
    • CMMC: Defense contractor cybersecurity maturity model that references NIST control structures

    These relationships allow different documents to share a common control vocabulary. Organizations operating across multiple compliance regimes can map their current security controls to various framework requirements, reducing duplication of effort and improving consistency.

    NIST 800-53 in Cloud and Industrial Digitalization Contexts

    Major cloud service providers publish mappings between their service controls and NIST 800-53 to support federal and regulated workloads. AWS, Microsoft Azure, Google Cloud Platform, and other providers document how their infrastructure, platform, and application services address 800-53 controls. These mappings illustrate how the catalog functions as a common reference across diverse technology stacks.

    For industrial and aerospace operations, this has practical implications. As factories, MRO facilities, and supplier networks rely more heavily on connected platforms, organizations increasingly model their technical and procedural safeguards using catalog-based references like 800-53. The catalog provides vocabulary for discussing:

    • Data protection requirements for production systems
    • Access control expectations for shopfloor applications
    • Communications protection standards for supplier integrations
    • Audit and accountability requirements for traceability systems

    From the perspective of a digital operations platform like Connect981, alignment with customers’ chosen catalogs is often part of integration and assurance discussions. Aerospace primes and defense contractors may specify security requirements using NIST 800-53 terminology, expecting their suppliers and platform vendors to understand and respond to that vocabulary.

    Using a common catalog lexicon simplifies communication between plant managers, IT security teams, and compliance stakeholders when evaluating:

    • Digital work instruction platforms and version control systems
    • Shopfloor execution and work order tracking applications
    • Supplier workflow integration and shared data visibility
    • Traceability systems and audit-ready documentation

    The catalog does not dictate specific technologies or architectures, but it provides a shared framework for articulating security requirements and evaluating whether proposed solutions address relevant cybersecurity risks and privacy risks.

    The image depicts a network of interconnected industrial manufacturing equipment featuring digital displays, showcasing advanced technology in a factory setting. This setup emphasizes the importance of security controls and risk management strategies, essential for protecting sensitive data and ensuring operational integrity in compliance with NIST 800 53 standards.

    Summary: Role of NIST 800-53 as a Security Controls Catalog

    NIST SP 800-53 Rev. 5 is a mature, widely recognized catalog of security and privacy controls, originally rooted in U.S. federal requirements and now broadly referenced across sectors. Its primary function is to provide a structured, detailed control vocabulary that can underpin risk management approaches, security architectures, and assurance programs. The catalog contains over 1,000 controls organized into 20 families, covering everything from access control and incident response to supply chain risk management and privacy protections.

    Organizations often relate NIST 800-53 to other frameworks, including ISO/IEC 27001 and the NIST Cybersecurity Framework, using mappings and harmonized taxonomies rather than treating them as mutually exclusive choices. This interoperability allows organizations to leverage existing controls to satisfy multiple requirements, communicate with different stakeholders using appropriate vocabulary, and maintain consistency across governance and technical documentation.

    This overview has focused on the conceptual and structural aspects of the catalog and its relevance to federal and industrial contexts. Understanding NIST 800-53 as a control catalog, rather than a prescriptive compliance mandate, clarifies its role in security discussions. For aerospace manufacturing and MRO operations, familiarity with this vocabulary supports effective communication with customers, partners, and internal stakeholders who reference these controls in their security requirements. The catalog provides common ground for discussing how digital platforms, supplier integrations, and connected operations protect organizational operations and national security interests.