Tag: manufacturing cybersecurity

  • What is ISO 27001? A Practical Overview for Aerospace and Industrial Operations

    What is ISO 27001? A Practical Overview for Aerospace and Industrial Operations

    Quick answer: what ISO 27001 is and why it matters in manufacturing

    ISO/IEC 27001 is the leading international standard for establishing, implementing, maintaining, and improving an information security management system. Published jointly by the International Organization for Standardization (ISO) and the International Electrotechnical Commission, the standard defines formal requirements for how organizations manage information security across people, processes, and information systems.

    In practical terms, ISO 27001 specifies what an organization must do to protect the confidentiality, integrity, and availability of information. It addresses cybersecurity, data protection, and privacy through a structured management system rather than through prescriptive technical controls. The standard is industry-neutral by design, applicable to any organization regardless of size or sector.

    For aerospace manufacturing, MRO operations, and industrial digitalization, ISO 27001 has become increasingly relevant. Production and supplier workflows now depend on connected, data-driven systems. ERP, MES, PLM, and supplier collaboration platforms like Connect981 create interdependencies that require structured governance over information security. The current version, ISO/IEC 27001:2022, reflects this reality by focusing on how organizations manage information security risks, not on specific technologies or tools.

    Key points to understand about ISO 27001:

    • It is a requirements standard, not an implementation guide
    • It applies to information in all forms: digital, paper-based, and verbal
    • It provides a comprehensive framework for managing information security risks
    • It supports integration with other ISO management system standards such as ISO 9001 and AS9100
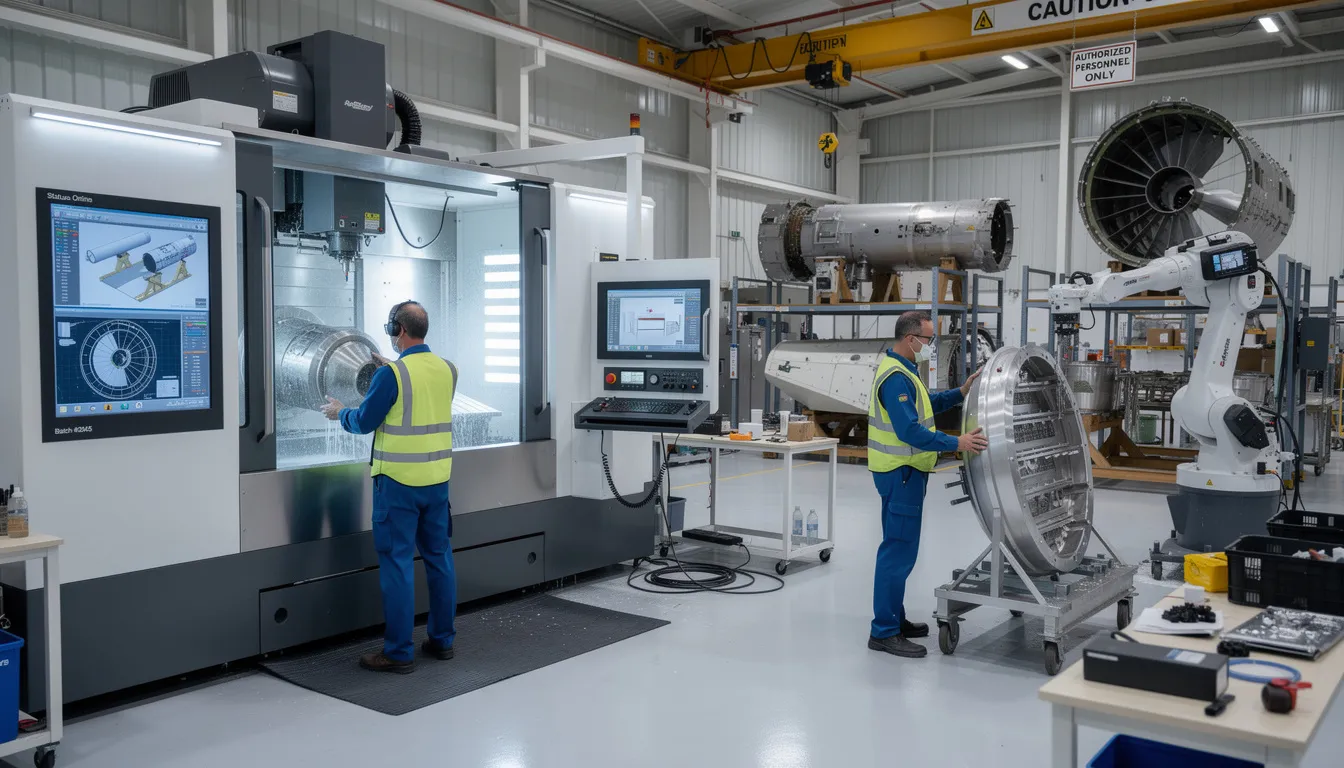
    The image depicts an aerospace manufacturing floor bustling with workers engaged in operating precision machinery, surrounded by advanced digital displays. This environment emphasizes the importance of information security management systems, as meticulous attention to security controls and risk management processes is crucial in safeguarding sensitive data and ensuring operational integrity.

    What does ISO/IEC 27001 actually define?

    ISO 27001 is a requirements standard. It specifies what an organization’s approach to managing information security must achieve. It does not dictate how to technically configure systems, which tools to deploy, or which specific security measures to implement.

    The standard covers several core areas:

    • Establishing an ISMS: Defining the scope, context, and governance structure for information security management
    • Implementing and maintaining the ISMS: Operating the management system through defined policies, procedures, and processes
    • Performing risk assessment and risk treatment: Identifying information security risks and determining how to address them
    • Defining roles and responsibilities: Assigning accountability for information security across the organization
    • Evaluating and improving ISMS performance: Monitoring effectiveness, conducting internal audits, and driving continual improvement

    ISO 27001 addresses information regardless of where it resides or what form it takes. For aerospace and industrial operations, this means the standard applies equally to design documentation stored in PLM systems, production data flowing through MES platforms, quality records maintained for AS9100 compliance, and supplier data shared through collaboration portals.

    The standard deliberately avoids prescribing specific products, tools, or detailed control techniques. An organization certified to ISO 27001 has demonstrated that its information security management processes meet the standard’s requirements. The actual controls selected depend on the organization’s risk assessment and treatment decisions.

    The scope of information security management in ISO 27001

    ISO 27001 defines information security through three fundamental properties, collectively known as the CIA triad:

    • Confidentiality: Protecting information from unauthorized disclosure
    • Integrity: Safeguarding information from improper modification
    • Availability: Ensuring information is accessible to authorized users when needed

    The scope of an ISMS is defined by the organization itself. In aerospace and industrial contexts, this scope might be expressed as “global aerospace manufacturing and MRO operations,” “production facilities in North America,” or “supplier collaboration platform and associated data flows.” Whatever the boundaries, they must be explicitly documented.

    Information assets within scope can include:

    • Design documentation and engineering drawings
    • Digital work instructions and revision-controlled procedures
    • Production data, including serial number tracking and build records
    • Quality records, inspection results, and nonconformance logs
    • Maintenance and repair histories for MRO operations
    • Supplier and customer data shared through collaboration portals
    • Configuration files for production systems, ERP integrations, and connected platforms

    When defining scope, organizations must consider both internal and external issues. Regulatory requirements such as AS9100, ITAR, FAA, and EASA create external constraints. Contractual commitments with primes or Tier 1 suppliers may specify information security expectations. Dependencies on cloud services or SaaS platforms, including operations software like Connect981, introduce additional considerations for how information is managed across boundaries.

    The scope determines which locations, processes, information systems, and interested parties fall under the ISMS. It defines what is governed, not how to secure it technically.

    The concept of an Information Security Management System (ISMS)

    An information security management system is the core concept at the heart of ISO 27001. It represents a formal management system that governs how an organization manages information security throughout the lifecycle of its information assets.

    An ISMS is not a piece of software or a collection of security tools. It is built on:

    • Policies that define the organization’s information security commitments
    • Procedures that translate policy into operational practice
    • Defined processes for identifying and treating information security risks
    • Roles and responsibilities assigned across the organization
    • Documented information that provides evidence of conformity and enables consistent operation

    The underlying model for an ISMS is the Plan-Do-Check-Act cycle, familiar to organizations already operating under ISO 9001 or AS9100. At a high level:

    • Plan: Establish the ISMS scope, conduct risk assessment, define objectives, and plan risk treatment
    • Do: Implement and operate the ISMS, including the risk treatment plan and selected security controls
    • Check: Monitor and measure ISMS performance, conduct internal audits, and perform management review
    • Act: Address nonconformities and drive continual improvement

    For manufacturing and MRO operations, the ISMS connects strategic decisions with operational practices. Leadership defines the organization’s information security policy and risk appetite. Those decisions then cascade into how production data is controlled, how documentation is managed across ERP, MES, and platforms like Connect981, and how supplier information flows are governed.

    In practice, the ISMS typically interfaces with other management systems. Quality management under AS9100, environmental management under ISO 14001, and occupational health and safety systems may all coexist. ISO 27001 focuses specifically on the information security aspects of operations, complementing rather than replacing those other systems.

    The image depicts an industrial control room where operators are actively monitoring digital systems and analyzing production data. This environment emphasizes information security management practices, reflecting the importance of ISO 27001 standards in managing security risks and ensuring the protection of sensitive data.

    High-level structure of ISO/IEC 27001

    ISO 27001 follows the Harmonized Structure used across ISO management system standards. This common architecture makes integration with quality management (ISO 9001, AS9100), environmental management (ISO 14001), and other management systems more straightforward.

    The standard is organized into three main components:

    Component

    Description

    Clauses 0–3

    Introduction, scope of the standard, normative references, and terms and definitions

    Clauses 4–10

    Core requirements for the ISMS

    Annex A

    Reference set of 93 information security controls

    Requirements Clauses 4–10

    • Clause 4 – Context of the organization: Understanding internal and external issues, determining interested parties and their requirements, defining the scope of the ISMS
    • Clause 5 – Leadership: Top management commitment, establishing the organization’s information security policy, assigning roles and responsibilities
    • Clause 6 – Planning: Addressing risks and opportunities, conducting information security risk assessment, planning risk treatment, setting information security objectives
    • Clause 7 – Support: Resources, competence, awareness, communication, and control of documented information
    • Clause 8 – Operation: Implementing and controlling the processes needed to meet information security requirements, executing the risk treatment plan
    • Clause 9 – Performance evaluation: Monitoring, measurement, analysis, and evaluation; internal audits; management review
    • Clause 10 – Improvement: Addressing nonconformities, implementing corrective actions, driving continuous improvement

    Annex A Controls

    Annex A of ISO/IEC 27001:2022 provides a catalog of 93 information security controls organized into four themes:

    Theme

    Focus Areas

    Organizational controls

    Policies, governance, asset management, access control policy, supplier relationships, incident management, business continuity, compliance

    People controls

    Human resource security, awareness, training, responsibilities during and after employment

    Physical controls

    Physical security, environmental security, equipment protection, secure areas

    Technological controls

    Endpoint security, access control, cryptography, operations security, communications security, secure coding, data masking, data leakage prevention, threat intelligence

    Selection and implementation of Annex A controls is not a fixed checklist. Organizations must justify their selection or exclusion of controls based on their information security risk management process. Full conformity with ISO 27001 requires meeting all applicable requirements in Clauses 4–10 and documenting the rationale for control selection.

    Relationship between ISO 27001 and ISO 27002

    ISO/IEC 27001 and ISO/IEC 27002 serve distinct but complementary purposes.

    Standard

    Purpose

    ISO/IEC 27001

    Requirements standard for an ISMS; certifiable

    ISO/IEC 27002

    Guidance document for information security controls; not certifiable

    ISO 27001 specifies what an ISMS must achieve. ISO 27002 provides detailed guidance and examples for how information security controls might be implemented. Each control listed in Annex A of ISO 27001:2022 has a corresponding section in ISO 27002:2022 with objectives, implementation guidance, and other information.

    An organization can pursue ISO 27001 certification through an accredited certification body. ISO 27002, by contrast, is a supporting code of practice. It helps organizations understand control objectives and consider implementation options, but it does not define additional requirements beyond what ISO 27001 specifies.

    In aerospace and industrial contexts, organizations typically use ISO 27001 to define the overarching management process and governance structure for information security. When more detail is needed on specific control areas, such as how to approach access control for production networks, documentation repositories, or supplier data flows, ISO 27002 serves as a reference.

    This article does not describe technical implementation or recommend specific technologies. The distinction between the two standards matters for understanding what certification demonstrates and where to look for additional guidance.

    Why ISO 27001 is referenced in manufacturing, aerospace, and industrial systems

    Digital transformation has fundamentally changed how manufacturing and MRO operations work. Production, quality, and supply chain processes have become information-intensive and interconnected. ERP systems, MES platforms, PLM tools, QMS software, and supplier collaboration platforms like Connect981 now form the operational backbone of aerospace production.

    This shift creates new information security risks. Production data, traceability records, work instructions, and supplier communications all flow through connected systems. Security incidents or data breaches can disrupt operations, compromise sensitive data, and expose organizations to regulatory consequences.

    ISO 27001 is referenced in manufacturing and industrial contexts because it provides a recognized structure for managing these information security risks. Organizations use the standard to demonstrate governance across:

    • Smart factory platforms and industrial IoT data flows
    • Integrated ERP, MES, PLM, QMS, and supplier collaboration systems
    • Documentation and traceability records required for AS9100, FAA, EASA, and ITAR-regulated operations
    • Multi-site and multi-supplier production networks

    Primes, Tier 1 suppliers, and regulators increasingly expect evidence of structured information security governance. ISO 27001 provides a security framework that is widely understood and internationally recognized. It offers a common language for discussing information security practices with business partners and customers.

    ISO 27001 complements rather than replaces sector-specific standards. AS9100 addresses quality management for aerospace. ITAR and export control regulations address controlled technical data. FAA and EASA requirements focus on aviation safety. ISO 27001 specifically addresses how information security is managed across all of these operational contexts.

    For organizations coordinating complex multi-site and multi-supplier production, an ISO 27001-aligned ISMS can provide a unifying structure. Even when not all entities in a supply chain are certified, the standard’s concepts support consistent governance over information security expectations across partners.
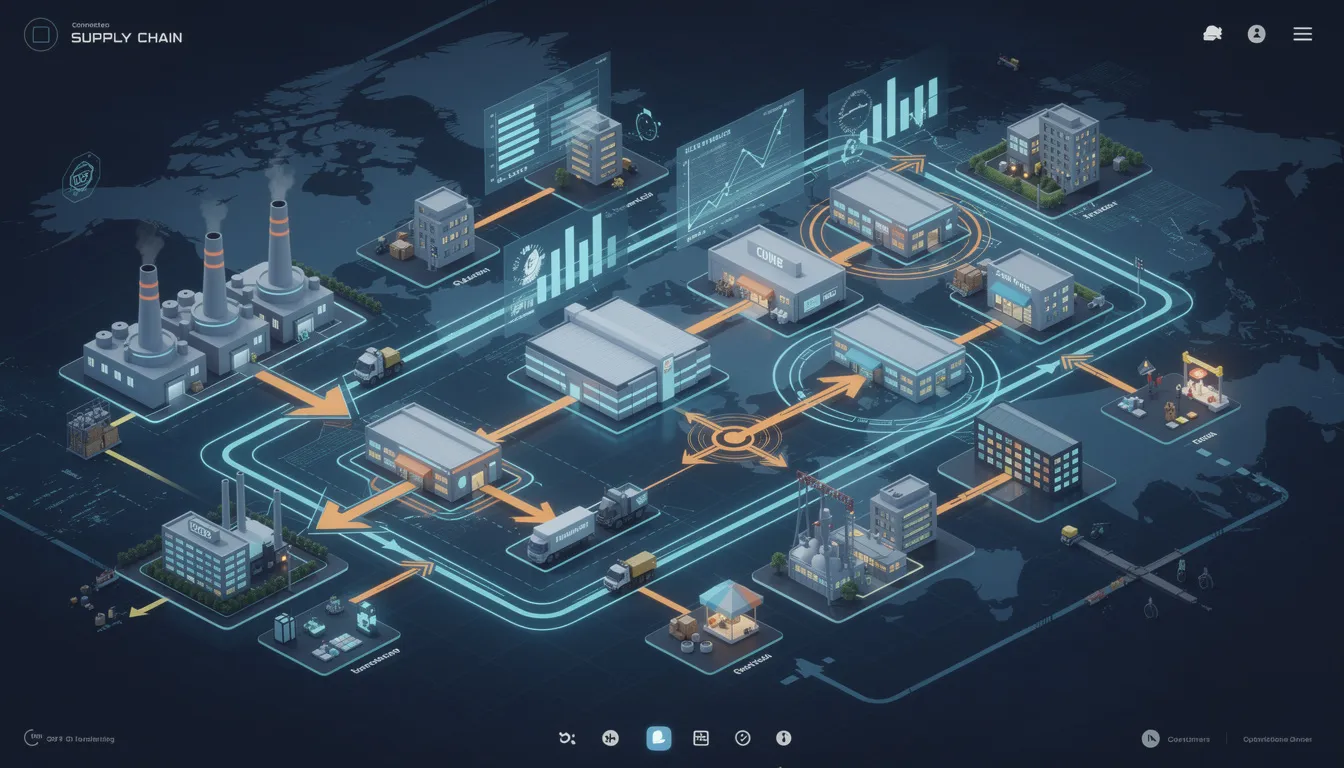
    The image depicts a connected supply chain visualization showcasing multiple facilities, each represented with data flows illustrating the integration of information security management systems. This visualization emphasizes the importance of ISO 27001 standards in managing information security risks and ensuring data protection across the supply chain.

    ISO 27001 in practice: certification, versions, and use in governance

    Certification process

    ISO 27001 certification is a formal verification by an accredited certification body that an organization’s ISMS conforms to the standard’s requirements. The certification audit typically occurs in two stages:

    • Stage 1: Documentation review to verify the ISMS is designed to meet requirements
    • Stage 2: On-site assessment to verify the ISMS is implemented and operating effectively

    Certification is valid for three years, subject to periodic surveillance audits. Recertification requires a full audit at the end of each cycle.

    Version history

    Version

    Key characteristics

    ISO/IEC 27001:2005

    Original international standard, based on BS 7799

    ISO/IEC 27001:2013

    Major revision with explicit leadership and planning clauses

    ISO/IEC 27001:2022

    Current version with Annex A reorganized to 93 controls across four themes, aligned with ISO/IEC 27002:2022

    Organizations certified under the 2013 version have transition timelines to update their ISMS to the 2022 edition. The structural changes primarily affect Annex A control organization rather than the core management system requirements.

    Approaches to using ISO 27001

    Organizations approach ISO 27001 in different ways depending on their objectives:

    • Internal reference framework: Using ISO 27001 concepts to structure information security governance without pursuing formal certification
    • Formal certification: Seeking certification to provide external assurance to customers, regulators, and business partners
    • Integrated management systems: Combining ISO 27001 with ISO 9001, AS9100, ISO 14001, or other standards under a shared governance structure

    ISO 27001 is generally not mandated by law, though specific jurisdictions or sectors may reference it. More commonly, it becomes a contractual requirement in supply chains where primes or customers expect evidence of information security governance.

    Relevance to digital operations platforms

    For organizations operating digital platforms like Connect981, alignment with ISO 27001 concepts supports customers’ own ISMS requirements. When production data, work instructions, quality records, and supplier collaboration flow through a shared platform, clear governance over that information becomes essential.

    A platform designed with information security governance in mind enables aerospace and industrial organizations to:

    • Maintain visibility over information assets across factories and suppliers
    • Support traceability and documentation control requirements
    • Provide evidence of information security practices for audits and customer reviews
    • Integrate with broader ISMS processes already in place

    ISO 27001 provides the reference framework. Operational platforms provide the capability to execute on information security requirements in practice. For organizations managing sensitive data, personally identifiable information, or ITAR-controlled technical data, this alignment matters.

    Information security controls continue to evolve as threats change and industrial systems become more connected. ISO 27001 offers a stable governance structure that adapts through its risk-based approach, supporting security posture improvements without requiring wholesale changes to the management system itself.

    For aerospace and industrial operations seeking to formalize information security governance, ISO 27001 provides a recognized starting point. Whether used as an internal framework or pursued through formal certification, the standard offers structure for managing information security in environments where production, quality, and supply chain data are increasingly interconnected.

    To explore how Connect981 supports governance over production data, documentation, and supplier workflows in aerospace and industrial operations, request a demo.

  • IEC 62443 Industrial Cybersecurity: A Standards-Based Overview for Manufacturing and OT

    IEC 62443 Industrial Cybersecurity: A Standards-Based Overview for Manufacturing and OT

    Executive summary: What IEC 62443 means for industrial and aerospace operations

    IEC 62443 is the primary international standard family for industrial automation and control systems cybersecurity, published jointly by the International Society of Automation (ISA) and the International Electrotechnical Commission (IEC). The series provides a structured, consensus-based framework for addressing cybersecurity risks across operational technology environments, including process plants, discrete manufacturing lines, and aerospace production and MRO facilities. Its focus on OT security distinguishes it from IT-centric standards like ISO/IEC 27001, reflecting the unique constraints of systems that must maintain real-time performance, safety, and continuous operation.

    The standard family is technology-neutral and sector-independent, meaning it applies equally to oil refineries, water treatment plants, power generation facilities, and aerospace manufacturing cells. Typical OT environments covered include SCADA systems, PLC-based control networks, and distributed control systems that govern everything from chemical process loops to CNC machine tools. This article provides a standards-based overview of IEC 62443: it explains the structure, concepts, and scope of the series, but does not offer prescriptive cybersecurity advice or design recommendations.

    From Connect981’s perspective, IEC 62443 aligns naturally with the operational concerns of aerospace manufacturing and MRO. Digital traceability, controlled workflows, and compliant operations depend on systems where integrity and availability are paramount. Understanding how the standard family defines requirements for industrial networks, control system solutions, and component security provides a useful reference point for organizations managing connected production environments across multiple sites and suppliers.

    Background and purpose of IEC 62443

    Origins in ISA99 and industrial control systems security

    The foundation of IEC 62443 traces back to 2002, when ISA formed the ISA99 committee to address emerging cybersecurity concerns for control systems in critical infrastructure sectors. At the time, industrial control systems were increasingly connected to enterprise networks, yet lacked the security frameworks that had developed for traditional IT systems. The committee brought together engineers, operators, and security professionals to develop consensus-based standards suited to operational technology environments.

    Adoption by the International Electrotechnical Commission

    In the late 2000s and early 2010s, the work of ISA99 was adopted by the IEC, creating the ISA IEC 62443 series recognized internationally. This adoption established a formal pathway for industrial organizations worldwide to reference a common set of requirements and terminology. The collaboration between ISA and IEC continues, with the ISA Global Cybersecurity Alliance and IEC Technical Committee 65 coordinating ongoing development and maintenance of the standard family.

    Purpose and lifecycle coverage

    The purpose of IEC 62443 is to define a common framework for securing industrial automation systems throughout their full lifecycle. This includes design, development, integration, operation, maintenance, and decommissioning. The series creates a shared language for asset owners, automation product suppliers, IACS service providers, and integrators when discussing security requirements, capabilities, and responsibilities. Rather than mandating uniform measures across all assets, IEC 62443 enables organizations to conduct security risk assessment and tailor requirements based on their specific operational risk management profiles and threat environments.

    Scope: What systems and environments IEC 62443 covers

    Defining Industrial Automation and Control Systems

    IEC 62443 defines Industrial Automation and Control Systems (IACS) as systems comprising combinations of hardware, software, networks, and personnel used to monitor, control, and automate industrial processes. This includes distributed control systems, SCADA systems, programmable logic controllers, safety instrumented systems, and the communication networks and software that support them.

    The scope spans multiple layers of industrial architecture:

    • Field devices such as sensors, actuators, and motor drives
    • Controllers including PLCs, RTUs, and embedded control modules
    • Network infrastructure connecting control system components
    • Supervisory systems for process monitoring and management
    • Engineering and maintenance workstations used for configuration and diagnostics

    Covered OT environments

    Typical OT environments addressed by IEC 62443 include process plants in chemicals and refining, discrete manufacturing lines, building management systems, electric power generation and distribution, water treatment facilities, transportation systems, and aerospace production and MRO operations. The standard focuses on cyber-related aspects of availability, integrity, and where relevant confidentiality of automation and control systems, distinct from but complementary to process safety standards.

    IEC 62443 applies to both new installations and legacy systems. Organizations can apply the framework to individual components, integrated systems, or complete facilities. From a Connect981 viewpoint, concrete examples include workstations running digital work instructions, automated test stands interfacing with control systems, specialized MRO benches, and manufacturing cells controlled via PLCs and industrial networks. Each of these represents a system under consideration where cybersecurity requirements must be defined and maintained.

    The image depicts an industrial manufacturing floor featuring robotic arms and control panels actively functioning within a production cell, highlighting the integration of industrial automation and control systems. This environment emphasizes the importance of control systems security and cybersecurity management in operational technology settings to protect critical infrastructure.

    Modular structure of the IEC 62443 standards family

    Four-part architecture

    IEC 62443 is organized into four main groups, each targeting specific roles and abstraction levels within the industrial ecosystem. This modular architecture allows organizations to adopt the most relevant documents first, rather than implementing the entire family simultaneously.

    The General group (part 1-x) establishes foundational terminology, concepts, and models for IACS security. The Policies and Procedures group (part 2-x) defines cybersecurity management system requirements for asset owners and IACS service providers. The System group (part 3-x) addresses system-level security risk assessment and system security requirements for integrated IACS. The Component group (part 4-x) covers secure development lifecycle requirements and technical security requirements for individual components.

    Key documents in the series

    IEC 62443-1-1 introduces the terminology, concepts, and models that form the vocabulary for the entire series. IEC 62443-2-1 specifies security program requirements for establishing and maintaining a cybersecurity management system within an industrial organization. IEC 62443-2-4 defines requirements for IACS service providers system integration and maintenance activities.

    IEC 62443-3-2 provides the methodology for security risk assessment and defining zones and conduits within a system. IEC 62443-3-3 specifies system security requirements and security levels for integrated control systems. IEC 62443-4-1 addresses secure development lifecycle requirements for product suppliers. IEC 62443-4-2 defines technical security requirements for components, establishing component security assurance expectations.

    Relationship between ISA and IEC naming

    The standard family uses parallel naming conventions between ISA and IEC publications. For example, ISA-62443-3-3 and IEC 62443-3-3 contain aligned content. The series collectively spans more than 800 pages of material across technical reports and normative standards. Parts are designed to be used together, but each is formally a separate standard with its own publication and revision cycle, allowing organizations to reference specific editions as required by their governance frameworks.

    Core concepts: Zones, conduits, security levels, and foundational requirements

    IEC 62443 introduces a set of core concepts to describe industrial cybersecurity in a structured, repeatable way. These concepts provide the vocabulary for defining requirements, assessing risks, and aligning expectations among key stakeholder groups without prescribing specific security technologies.

    System under Consideration

    The System under Consideration (SuC) defines the boundary of what is being analyzed or specified. This might be a single production line, a SCADA system for a utility, or a multi-cell aerospace assembly area. Establishing the SuC is a prerequisite for conducting risk analysis and defining security controls appropriate to the operational context.

    Zones and conduits

    Zones are logical groupings of IACS assets that share similar security requirements. A zone might encompass a high-criticality flight-control component machining cell, a lower-criticality facility monitoring network, or an enterprise-facing data collection system. Assets within a zone share a common target security level.

    Conduits are controlled communication paths linking zones. Security requirements for data flows through conduits are defined to manage the transfer of information between areas with different security postures. This approach supports network segmentation strategies that limit the propagation of cyber threats across industrial networks without requiring uniform measures throughout the entire facility.

    Security levels

    IEC 62443 defines security levels (SL 0 through SL 4) as a way to express the required resistance against classes of threat actors. SL 1 addresses protection against unintentional or accidental misuse. SL 2 addresses intentional attacks using simple means and moderate resources. SL 3 addresses sophisticated attacks with significant resources. SL 4 addresses advanced persistent threats with extensive capabilities. Organizations specify target security levels (SL-T) based on risk assessment, and systems or components provide capability security levels (SL-C) that indicate their inherent security features.

    Seven foundational requirements

    Parts 3-3 and 4-2 of the series define seven foundational requirements that structure the detailed system security requirements and technical security requirements:

    • Identification and Authentication Control: Establishing and verifying identity of users, devices, and software.
    • Use Control: Enforcing authorized privileges and least-privilege principles.
    • System Integrity: Protecting systems and data from unauthorized modification.
    • Data Confidentiality: Ensuring sensitive information is protected from unauthorized disclosure.
    • Restricted Data Flow: Controlling and monitoring information flows between zones.
    • Timely Response to Events: Detecting and responding to security incidents.
    • Resource Availability: Ensuring critical systems remain available for intended operations.

    These foundational requirements connect high-level IACS security program requirements with concrete system and component-level expectations.

    Distinguishing IT and OT security in IEC 62443

    Fundamental differences in priorities

    Traditional IT systems environments prioritize data confidentiality, integrity, and availability in roughly that order. Enterprise networks, office applications, and cloud services can typically tolerate brief outages for patching and updates. In contrast, OT systems and operational technology environments prioritize availability and safety above all else. Control systems governing manufacturing processes, utility operations, and safety-critical functions must remain operational continuously. Unplanned downtime in OT environments can disrupt production, damage equipment, or create safety hazards.

    IEC 62443 is explicitly designed around these OT constraints. Long equipment lifecycles, deterministic communication requirements, safety interlocks, and the need for continuous operation shape how security measures are interpreted and applied. The standard recognizes that aggressive patching cycles and frequent system restarts, common in IT environments, may be impractical or dangerous in operational technology environments.

    Shared concepts with OT-specific interpretation

    The standard family still addresses IT security concepts such as authentication, logging, data protection, and access control. However, IEC 62443 interprets these concepts in a way that reflects OT-specific requirements and risk trade-offs. For example, identification and authentication controls must function reliably without introducing latency that could disrupt real-time control loops.

    Aerospace and MRO examples

    In aerospace manufacturing and MRO operations, the IT/OT distinction manifests in concrete scenarios. A CNC machine tool cell where unplanned downtime disrupts flight hardware deliveries represents a high-availability OT environment. A test stand where control software interacts with high-energy systems subject to process safety standards requires careful integration of cybersecurity and safety requirements. Shopfloor terminals running digital work instructions may interface with both MES and ERP systems (IT) and machine controllers (OT), creating convergence points where both perspectives apply.

    IEC 62443 provides a vocabulary to align IT security teams, OT engineers, and production management. The standard defines roles and shared concepts without prescribing a particular organizational structure, enabling organizations to coordinate control systems cybersecurity standards across functions.

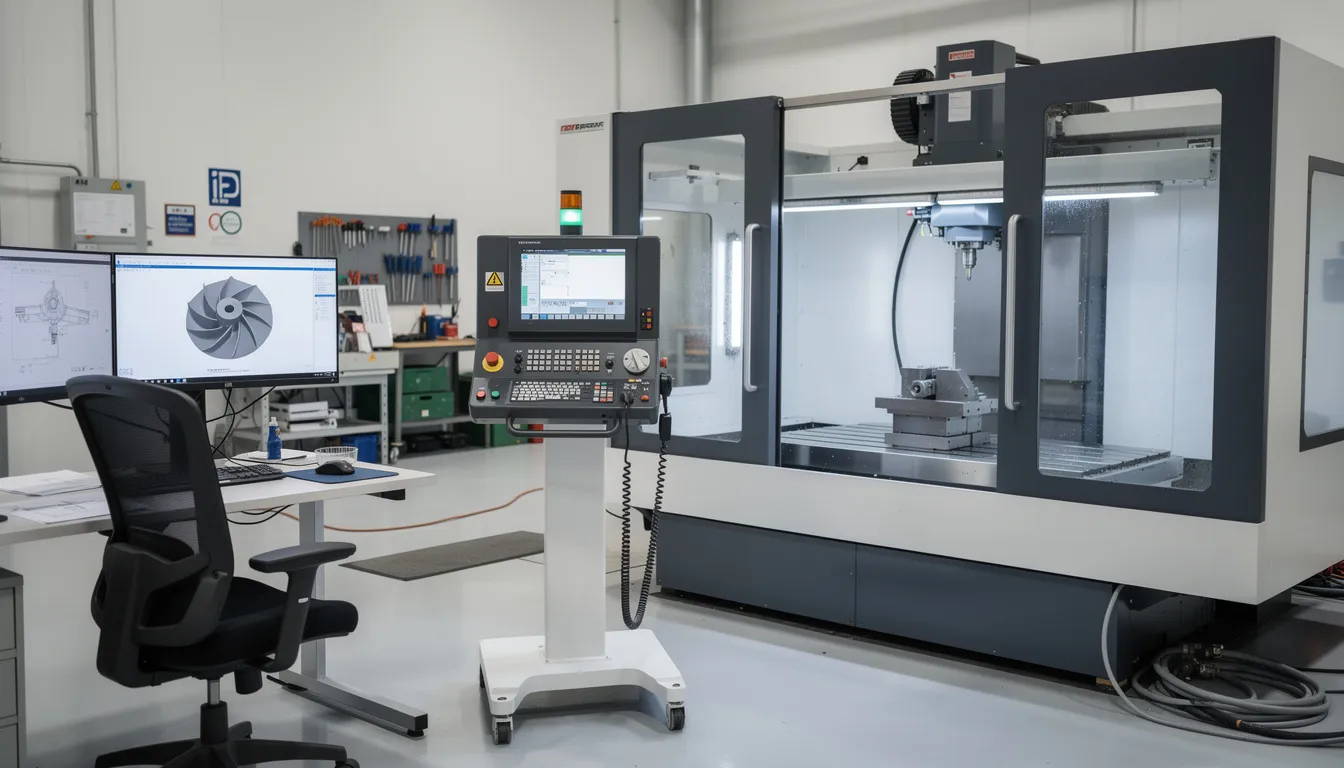
    The image depicts an aerospace CNC machining center featuring an operator workstation and an industrial control panel, illustrating a sophisticated setup for industrial automation. This environment emphasizes the importance of control systems security and operational technology, highlighting the need for robust cybersecurity measures in critical infrastructure.

    Relevance of IEC 62443 for manufacturing, aerospace, and MRO operations

    Connectivity and convergence in modern manufacturing

    IEC 62443 is particularly relevant for modern manufacturing and aerospace operations where OT systems are increasingly connected to enterprise IT, supplier networks, and cloud-based analytics platforms. Industry 4.0 initiatives have expanded the attack surface for industrial automation control systems, making structured approaches to OT security essential. The standard provides a framework for addressing cybersecurity risks that arise when production systems, work instructions, and quality data flow across previously isolated boundaries.

    Supporting key manufacturing concerns

    The framework supports several operational concerns central to aerospace manufacturing and MRO:

    • Maintaining predictable production schedules and turnaround times by protecting control systems that govern manufacturing execution
    • Protecting integrity of process parameters, digital work instructions, and test results that feed quality and compliance records
    • Ensuring traceability and auditability of control changes across facilities and suppliers participating in complex programs

    Connection to aerospace regulatory and quality frameworks

    Aerospace operations already navigate regulatory and quality frameworks including AS9100, FAA and EASA oversight, NADCAP audits, and ITAR requirements. IEC 62443 provides complementary IACS-focused expectations for critical infrastructure protection, but does not replace sector-specific regulations. The standard’s structured approach to defining zones, security levels, and security requirements can support regulatory compliance efforts by establishing consistent terminology and expectations for industrial automation and control systems security.

    Connect981 perspective on IEC 62443 alignment

    From Connect981’s perspective, a unified operations layer that connects ERP, MES, documentation, and shopfloor execution benefits from alignment with IEC 62443 concepts. Clear definition of systems and zones across multiple plants and suppliers supports consistent governance. Structured handling of configuration data and production records feeding traceability and quality systems reflects the integrity requirements central to the standard. Integration of supplier data and remote services into the broader OT and IT systems landscape can reference the conduit and zone concepts to maintain appropriate security controls.

    Concrete manufacturing scenarios illustrate this relevance. A multi-site wing assembly program with shared routing and inspection workflows spans multiple zones, each with defined security requirements. An MRO facility managing serialized components with long service histories and distributed data sources must maintain control system solutions that protect the integrity of maintenance records across the component lifecycle.

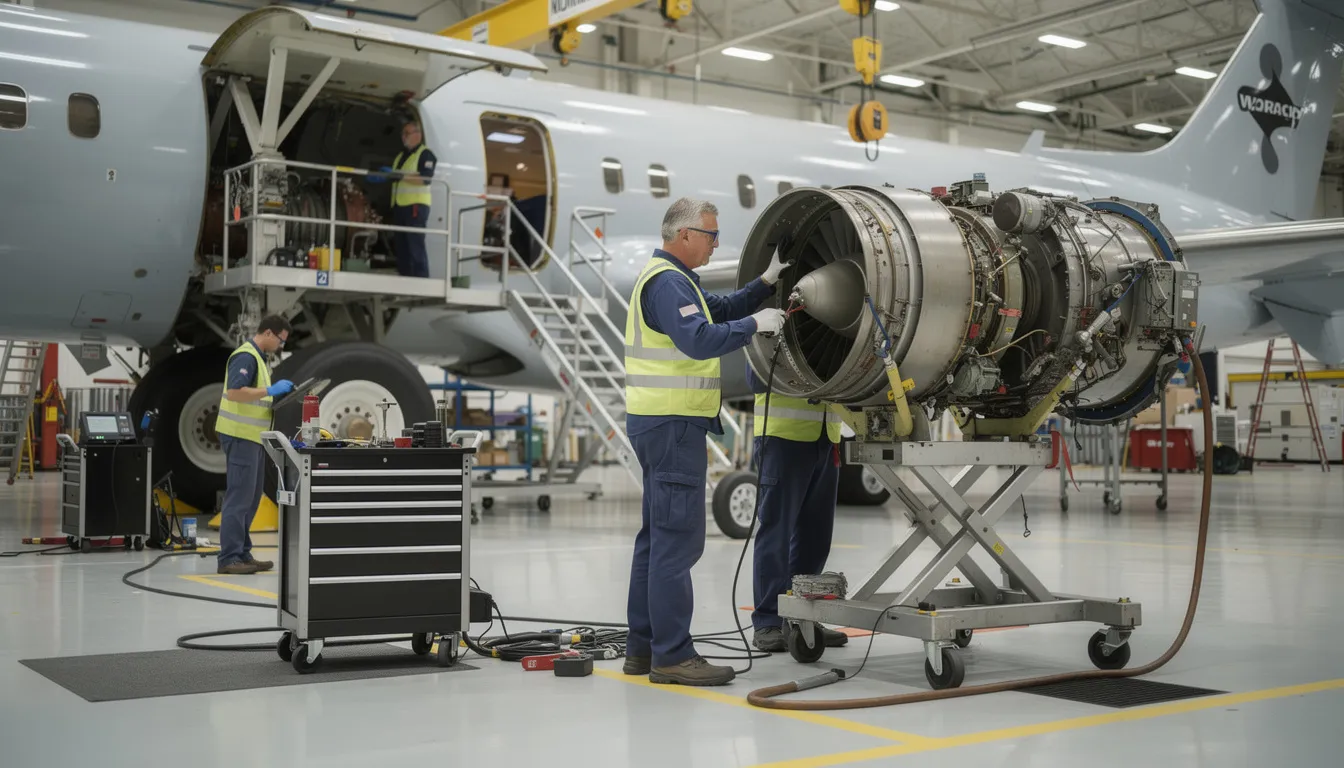
    The image depicts MRO technicians diligently working on various aircraft components within a spacious hangar environment, showcasing their expertise in maintaining control systems and ensuring the safety of critical infrastructure. The scene highlights the importance of industrial automation and control systems in aviation maintenance, emphasizing the need for robust cybersecurity practices to protect operational technology.

    Roles and responsibilities across the industrial ecosystem

    Stakeholder categories in IEC 62443

    IEC 62443 assigns expectations to different stakeholder groups involved with IACS. The standard recognizes that industrial cybersecurity is not the responsibility of any single party, but rather emerges from coordinated efforts across asset owners, product suppliers, system integrators, and service providers.

    Asset owner responsibilities

    Asset owners, typically the organizations operating industrial facilities, define required security levels for their systems based on security risk assessment. They establish and maintain a cybersecurity management system, coordinate cybersecurity practices across sites, and implement continuous monitoring and response capabilities. Asset owners are responsible for ensuring that the combined system meets target security levels, even when integrating components from multiple suppliers.

    Product supplier responsibilities

    Product suppliers, including OEMs of control system components, design and document component security capabilities in line with IEC 62443-4-1 and 4-2. Secure development lifecycle requirements ensure that products are designed with security in mind from the outset. Suppliers document the security levels components can achieve and provide information needed for integration and operation.

    Integrator and service provider responsibilities

    System integrators combine components from multiple suppliers into systems that meet defined security requirements. They are responsible for ensuring that the integrated system achieves the target security levels specified by asset owners. IACS service providers, including those providing maintenance, engineering, and remote support, must meet requirements defined in IEC 62443-2-4 for documentation, testing, and lifecycle support.

    Coordination in aerospace environments

    In aerospace manufacturing and MRO environments, multiple parties must coordinate around consistent terminology and requirements. Internal engineering teams, external equipment OEMs, specialized MRO service providers, and digital platform vendors all contribute to the security posture of connected production systems. IEC 62443 provides the shared vocabulary that enables this coordination without prescribing specific organizational structures.

    Integration with broader standards and governance frameworks

    IEC 62443 is often used alongside other international and sectoral standards. ISO/IEC 27001 addresses information security management for enterprise IT systems. The NIST Cybersecurity Framework provides a risk-based approach applicable across sectors. Process safety standards such as IEC 61511 address functional safety for industrial processes. Each covers distinct but related domains.

    IEC 62443 focuses specifically on IACS and OT, while ISO/IEC 27001 primarily addresses information security for enterprise IT. Organizations commonly map requirements between these frameworks to achieve unified governance across IT and OT environments. The zone and conduit concepts from IEC 62443 can complement higher-level risk and compliance frameworks, providing specific vocabulary for industrial networks and critical systems within broader governance structures.

    For aerospace operations already managing AS9100, FAA, EASA, and ITAR compliance, IEC 62443 offers additional structure for addressing cybersecurity risks in production and MRO environments. The standard’s terminology for security levels, foundational requirements, and system security assurance can support audit readiness and consistent reporting across industry sectors.

    From the perspective of a connected operations platform like Connect981, aligning data models and workflows with IEC 62443 concepts supports consistent reporting, documentation, and audit readiness across factories, MRO facilities, and suppliers. The framework provides a reference for coordinating digital workflows and external networks without creating conflicts with existing regulatory compliance requirements.

    Practical considerations and limitations when applying IEC 62443

    Phased adoption

    The IEC 62443 series is extensive, covering hundreds of pages across multiple parts. Organizations typically phase their adoption according to role and priority. Asset owners may begin with IEC 62443-2-1 to establish a cybersecurity management system, while product suppliers focus on IEC 62443-4-1 and 4-2 for secure development and component requirements. This modular approach allows organizations to adopt the most relevant documents first without requiring simultaneous implementation of the entire family.

    Contextual factors in industrial environments

    Industrial plants and aerospace operations present contextual factors that affect how IEC 62443 requirements are interpreted and applied. Prevalence of legacy control systems with limited security capabilities, heterogeneous vendor landscapes spanning multiple generations of equipment, and multi-decade asset lifecycles all influence implementation approaches. The standard family intentionally leaves room for organizations to interpret and implement requirements in line with their own risk governance and operational constraints.

    Ongoing evolution of the standard

    Different parts of the standard family mature at different times, with revisions and new technical reports periodically published through the IEC and ISA. Organizations must track applicable editions and updates to ensure their practices remain aligned with current expectations. The ISA Global Cybersecurity Alliance continues to coordinate development and provide guidance on applying the series across industry sectors including the industrial process sector, discrete manufacturing, and critical infrastructure.

    Conclusion: IEC 62443 as a reference point for secure industrial operations

    IEC 62443 provides a structured, role-aware framework for describing and specifying cybersecurity requirements for industrial automation and control systems across industries. The series establishes clear scope, modular structure, and core concepts including zones, conduits, security levels, and seven foundational requirements. The explicit distinction between IT and OT security ensures that the framework addresses the unique constraints of critical functions in operational technology environments.

    For manufacturing, aerospace production, and MRO operations, IEC 62443 offers particular relevance. Digital traceability, controlled workflows, and cross-site consistency depend on systems where integrity and availability are paramount. The framework provides vocabulary and expectations that support coordination among engineering, operations, suppliers, and enterprise governance functions managing critical assets across complex programs.

    From Connect981’s perspective, standards such as IEC 62443 form a foundational reference for designing and governing digital industrial operations. The framework enables alignment between operational technology security requirements and the connected workflows that define modern aerospace manufacturing and MRO, supporting organizations as they maintain control system solutions that meet evolving expectations for industrial cybersecurity.